The National Cyber Emergency Response Team (National CERT) has instructed government staff to employ only VPNs that have been approved by their departments when accessing official systems from outside the office, cautioning that exposing those services directly to the internet could make them vulnerable to attacks.
The National Cybersecurity Handbook 2026-27 notes that government-provided VPNs establish protected links for remote employees, helping shield data from unauthorized access and interception.
According to the handbook, workers must rely on VPN services sanctioned by their agencies, keep strong login credentials, and end remote sessions as soon as official duties are finished. They are also directed to notify IT or cybersecurity teams if VPN connections become unstable or repeatedly drop.
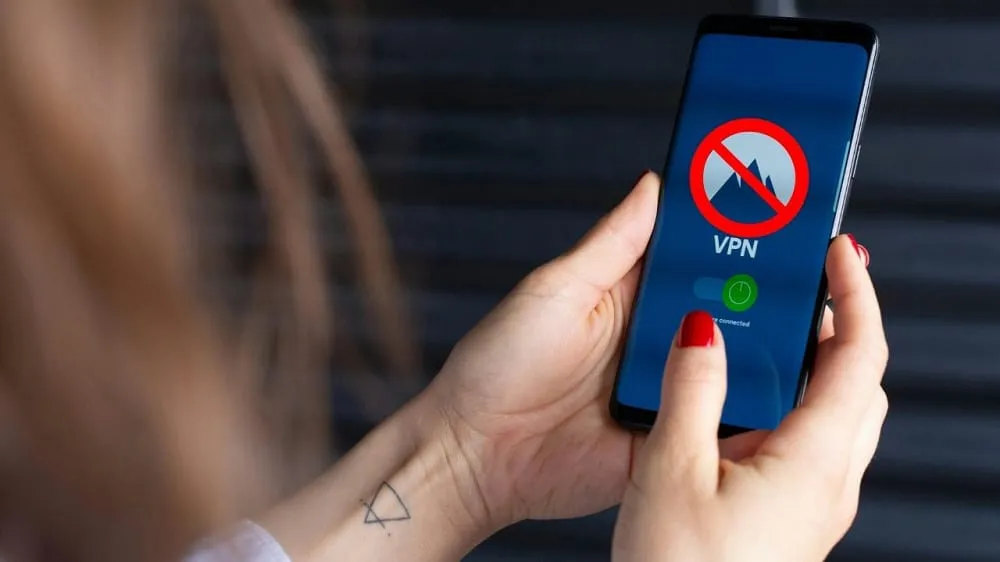
Staff have been warned not to use any unauthorized VPNs or proxy apps for work purposes. The guidance also bans disabling antivirus programs, firewalls or other endpoint protection tools to boost VPN performance, leaving VPN sessions open on unlocked devices, or sharing login details.
The handbook cautions that ignoring secure remote-access procedures could open government networks to automated brute-force attacks, ransomware aimed at internal servers, and persistent backdoors that might allow long-term espionage.
These directives are part of wider cybersecurity strategies outlined for federal and provincial governments as well as public-sector bodies.