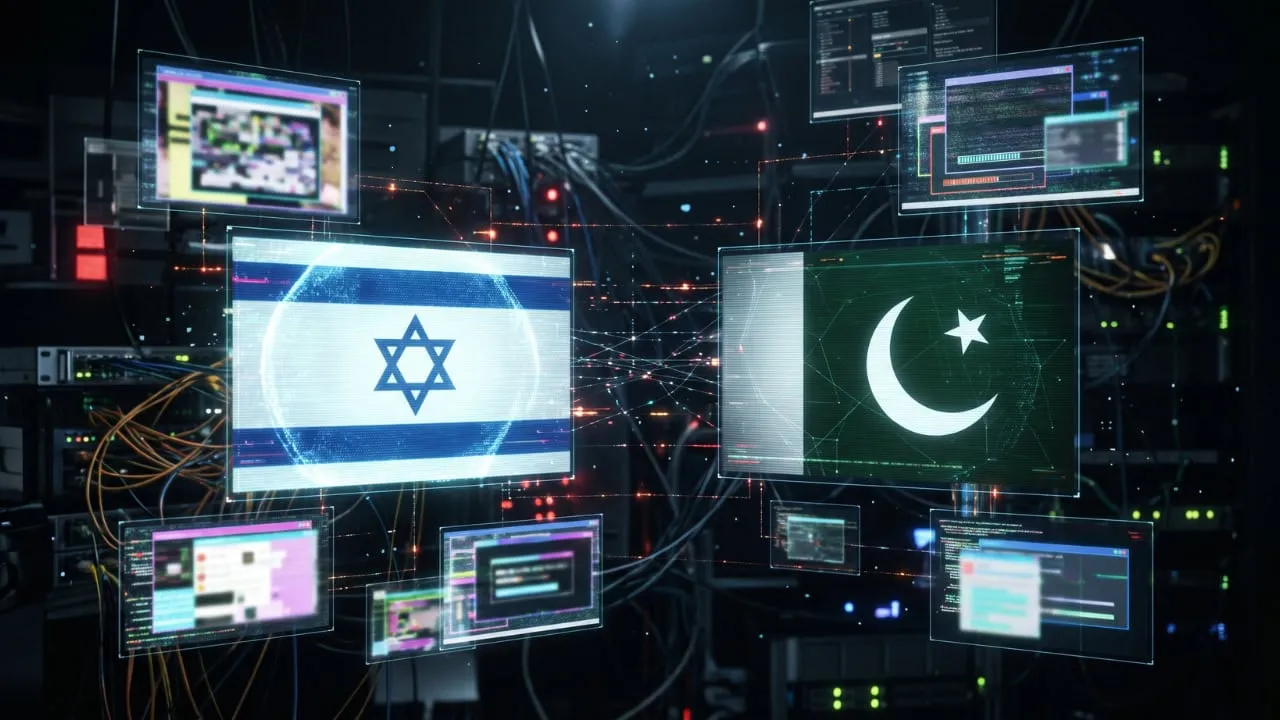
On October 15, the University of Toronto's Citizen Lab published a troubling study that exposed a large-scale cyber threat using the online ad ecosystem. The paper says an Israeli firm called Discover-Tech facilitated device hacks via ad placements, and it identified Pakistan as one of the most heavily targeted nations worldwide.
Israeli Spyware Ads Massively Targeting Pakistan
Researchers examined close to four billion bidding entries from Discover-Tech's advertising platform, covering the period from March to June 2026. They found that about 19% of those bids contained hidden scripts designed to deliver malicious code.
Pakistan came in second globally for such malicious bids, with roughly 139 million attempts. Only Yemen was higher, with around 457 million bids. Over 100,000 of the dangerous ads appeared on the popular Pakistani site whatmobile.com.pk, and the campaign also reached government-run networks in the country, though the report does not specify which ones.
The Silent Threat of AdFection
Citizen Lab labels this covert technique "AdFection". Discover-Tech sold ad inventory that embedded concealed attack code, allowing a device to become infected simply by displaying the ad, without any user click.
The firm acted as a conduit between spyware developers and the ad system, delivering code created by Candiru, now operating as Integrity Labs. The same method was previously used to compromise at least 45 devices at Al Jazeera during 2024 and 2025.
The Pindi Connection & Future Risks
Investigators also found a user alias "Pindi" who accessed Discover-Tech's Controlium platform exclusively from Pakistan. Citizen Lab says this login alone does not prove a link to any particular mercenary spyware group or confirm targeted attacks.
Since an ad impression does not guarantee a successful intrusion, the data cannot show whether specific individuals in Pakistan were chosen for infection. Nevertheless, researchers call for prompt investigations, noting the campaign's scale presents a serious cybersecurity danger for anyone on the affected networks.