Tim Hortons App Privacy Controversy Explained
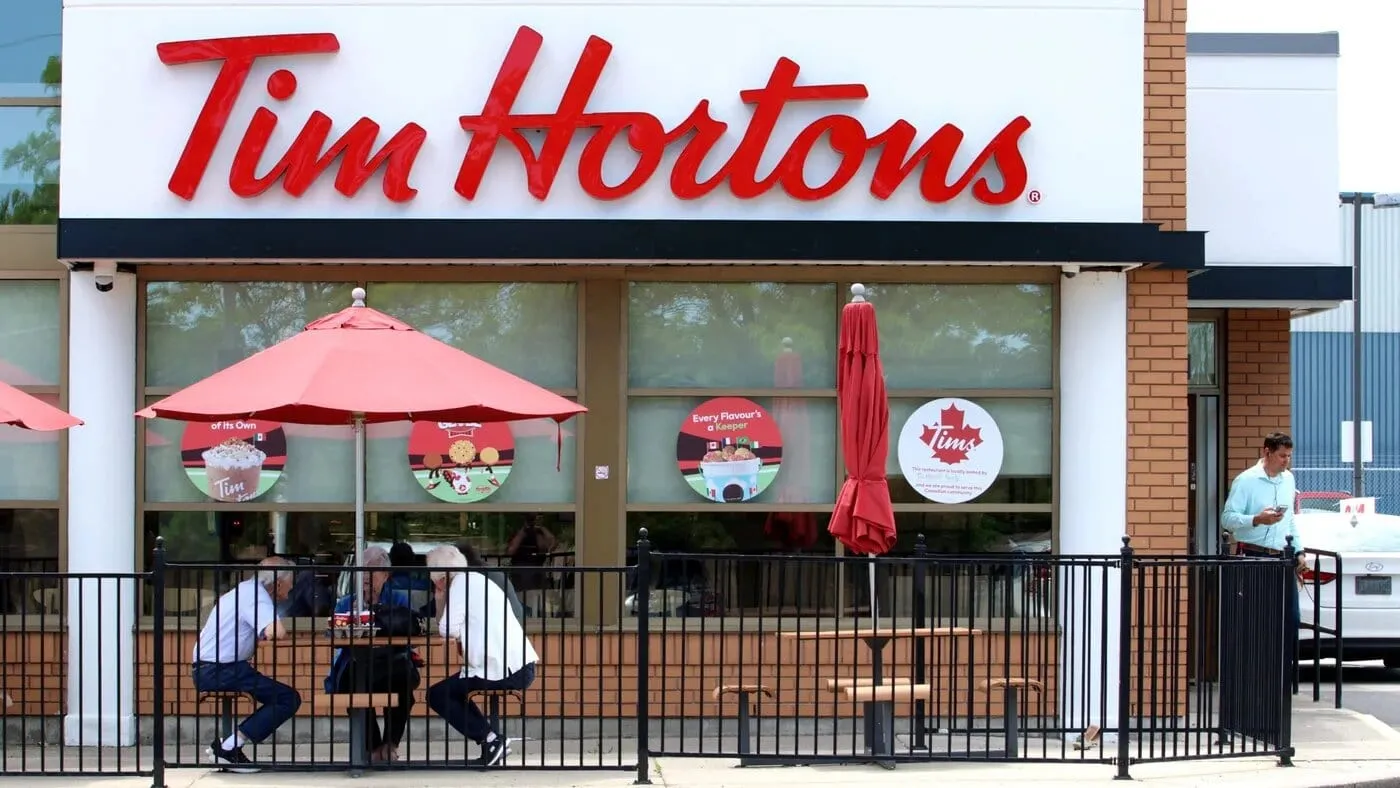
Tim Hortons faces intense public scrutiny following revelations that its official mobile application shares sensitive user information with an external technology company based in Israel. On Tuesday, a prominent Canadian advocacy organization raised serious alarms regarding this data sharing arrangement and demanded that the popular coffee and doughnut chain terminate the partnership instantly. The core of the issue centers on how customer data gathered through the ordering software travels to third-party entities without transparent consent mechanisms.
The controversy emerged into the public sphere after extensive digital forensic analysis revealed the destination of the harvested metrics. Users across Canada who download and use the platform for purchases and loyalty rewards routinely hand over smartphone diagnostics that security researchers argue go far beyond standard operational needs. The involvement of a foreign enterprise with direct roots in military cyber operations has amplified public unease about corporate data handling practices within the retail food sector.
How the Data Sharing Discovery Happened
Canadians for Justice and Peace in the Middle East publicly identified the recipient of the information as Forter, an enterprise specializing in digital fraud prevention. Forter was established by individuals who previously served in Unit 8200, which functions as the signals intelligence and cyberwarfare division of the Israeli military. The advocacy collective pinned down the identity of the firm after consulting directly with University of Calgary researcher Joel Reardon.
Academic researchers and investigative journalists have spent months tracking hidden software development kits embedded inside popular consumer applications. The findings regarding Tim Hortons were originally highlighted during an investigative report broadcast by the Canadian Broadcasting Corporation on November 13. While that initial broadcast outlined the general flow of telemetry to outside entities, it initially omitted the specific name of the foreign security contractor involved, leading to questions from watchdog groups.
Specific Types of Data Collected by the Tim Hortons App
The digital audit conducted by researchers demonstrated that the software extracted a wide variety of personal smartphone indicators from unsuspecting patrons. The information transmitted to external servers included unique device identifiers assigned to individual handsets, detailed camera specifications, and precise details concerning nearby Wi-Fi networks. Security analysts classify these specific data points as highly sensitive because they allow for sophisticated tracking and fingerprinting of mobile hardware.
Joel Reardon described the sheer volume and depth of this collection process as going far beyond the pale of normal business operations. These technical revelations directly challenged consumer assumptions about privacy when interacting with restaurant software designed primarily for placing beverage orders and collecting reward points. The granularity of the telemetry harvested by the platform left privacy advocates demanding immediate transparency from corporate executives regarding every external entity with access to customer files.
Advocacy Group Demands Immediate Termination of Partnership
Michael Bueckert, who serves as the vice president of Canadians for Justice and Peace in the Middle East, issued harsh public criticism regarding the corporate data practices. He asserted that patrons purchasing morning coffee should never have their confidential technical metrics routed to an overseas cyber technology firm whose foundational infrastructure stems from foreign military alumni. The organization focused heavily on the background of the founders and their institutional ties to intelligence apparatuses accused of engaging in systemic human rights violations.
The campaign led by the advocacy collective calls for a complete severance of all contractual ties between the restaurant chain and the fraud prevention vendor. Representatives argued that corporate reliance on security vendors with intelligence backgrounds exposes domestic consumers to geopolitical surveillance chains without their explicit knowledge. The public appeal also highlighted previous actions taken by other major technology conglomerates against similar state-linked entities.
"Canadians ordering coffee should not have their unique and sensitive user data shared with an Israeli cyber-tech company whose infrastructure was built by alumni of a foreign military intelligence agency engaged in human rights violations," Michael Bueckert said.
In mid-September 2025, Microsoft took affirmative steps to disable specific cloud computing and artificial intelligence services used by Unit 8200. That corporate decision by the technology giant followed accumulating evidence corroborating reports that the intelligence unit's specialized technology facilitated mass surveillance initiatives directed against Palestinians. Watchdog organizations have leveraged this international precedent to argue that commercial consumer brands should distance themselves from vendors sharing personnel with such specialized divisions.
Corporate Response and Prior Privacy Violations
In response to the mounting public pressure and media inquiries, corporate representatives for Tim Hortons defended their technical architecture by emphasizing the necessity of fraud prevention. The company stated to the Canadian Broadcasting Corporation that the information was gathered exclusively to safeguard user accounts, verify legitimate transactions, and block fraudulent payment attempts. Furthermore, corporate officials asserted that the harvested metrics were never used for advertising or marketing campaigns under any circumstances.
The restaurant chain insisted that external partners remained strictly prohibited from selling the information supplied through the software integration. Executives maintained that customer personal data was never monetized or transferred to unrelated brokers. Despite these assurances, the brand carries a troubled history regarding consumer confidentiality matters that predates the current controversy.
In 2022, federal and provincial privacy authorities in Canada delivered a scathing ruling finding that the exact same mobile application tracked extensive location data of users continuously without obtaining proper consent. That historical infraction forced the company to delete vast repositories of illegally gathered location history and overhaul its internal compliance protocols. The recurrence of invasive data practices has left consumer protection advocates skeptical of current corporate safeguards.
Criticism of Media Omission and Next Steps for Consumers
The controversy also involved a procedural dispute regarding how the news media reported the initial findings. Canadians for Justice and Peace in the Middle East publicly questioned the decision by the Canadian Broadcasting Corporation to omit the name of the Israeli software firm from its initial November 13 broadcast. The advocacy association formally raised this editorial omission with the broadcaster internal ombudsman to demand greater transparency in future reporting on foreign corporate partnerships.
As the debate continues to unfold, regular patrons face difficult choices regarding how they interact with retail ordering platforms on their smartphones. Digital security specialists consistently recommend reviewing application permissions within mobile operating system settings and revoking access to location services, local network states, and hardware identifiers whenever possible. Observers will continue monitoring whether the restaurant chain yields to public pressure and replaces its current fraud detection vendor with a domestic alternative.