Why the AI Industry is Prime Target for Honey Trap Schemes
The artificial intelligence sector faces a growing counterintelligence threat as foreign intelligence agencies and malicious actors shift their focus from government offices to private technology firms. Following the high-profile resignation of NVIDIA Chief Executive Officer Jensen Huang amid allegations involving a Chinese spy, security professionals warn that the entire sector remains exposed to sophisticated deception operations. While past espionage efforts focused heavily on military officials, politicians, and intelligence personnel, the most sensitive intellectual property and strategic hardware now reside within private corporations designing chips, training large language models, and building critical infrastructure.
Industry insiders emphasize that artificial intelligence founders and corporate employees lack the specialized counterintelligence training traditionally provided to government officials holding security clearances. This mismatch creates an attractive opening for foreign intelligence services seeking access to restricted hardware, product roadmaps, customer lists, and export decisions. Because artificial intelligence has transformed rapidly into a critical national security sector, corporate boardrooms and research laboratories now function as frontline targets in global espionage.
Understanding the Jensen Huang NVIDIA Case
The situation involving former NVIDIA Chief Executive Officer Jensen Huang brought the hidden risks of corporate espionage into public view. Reports emerged regarding an alleged relationship with Alice Huang, a neocloud executive based in Singapore who faced accusations of operating as a Chinese spy. Investigators allege that she facilitated the unauthorized movement of restricted NVIDIA computer chips valued at billions of dollars into China. In response to these allegations, Huang stepped down from his position, prompting an independent review by the company board alongside a parallel investigation by the Federal Bureau of Investigation into potential foreign targeting.
This incident demonstrates how quickly a corporate leader can become compromised when traditional security protocols fail to account for personal relationships. Obtaining access to a chief executive provides an adversary with the most direct route to proprietary technology, strategic partnerships, and government policy decisions. The subsequent fallout at NVIDIA highlights the severe operational and legal consequences companies face when high-ranking officials are successfully targeted by foreign intelligence operations.
How Modern Honey Traps Target AI Founders and Employees
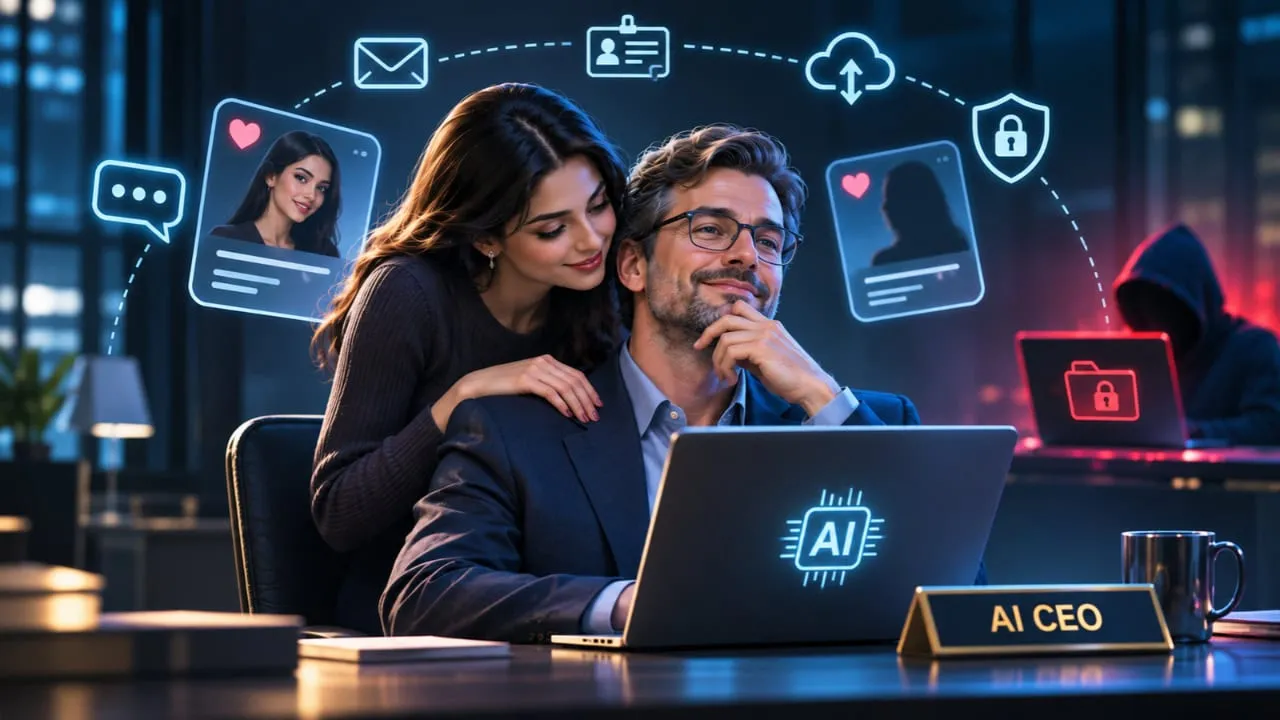
The threat profile extends far beyond chief executive officers to encompass board members, researchers, executive assistants, and any employee holding administrative or technical access to sensitive information. Furthermore, these recruitment efforts rarely manifest as traditional romantic encounters. According to Aaron Brown, a former senior executive at the Central Intelligence Agency and current founder of software company Lumbra, friendship remains the oldest and most effective honey trap method in existence. Attackers frequently infiltrate corporate networks by posing as investors, potential customers, recruiters, or industry consultants whose inquiries appear entirely legitimate.
Brown noted that these schemes succeed because perpetrators take time to build trust and make targets feel comfortable discussing sensitive topics without raising immediate suspicions. Perry Carpenter, a cybercriminologist and chief deception strategist at security firm KnowBe4, pointed out the inherent irony of artificial intelligence leaders automating complex human tasks while remaining susceptible to basic social engineering. Adversaries bypass complex digital firewalls simply by cultivating relationships with individuals who possess the authority to open physical or digital doors.
The Role of Artificial Intelligence in Scaling Deception Operations
Modern technology has drastically reduced the cost and time required for intelligence agencies to mount sophisticated social engineering campaigns. Historically, executing a convincing honey trap required months or years of intensive background research, persona development, and meticulous planning. Today, malicious actors use artificial intelligence tools to study prospective targets, generate fraudulent social media profiles, construct elaborate fictional backgrounds, and even produce convincing deepfake voice communications.
Carpenter explained that while artificial technology assists in establishing and sustaining these fabricated identities, the actual deception ultimately relies on manipulating human psychology and exploiting the natural desire of individuals to feel understood. Because the interactions feel authentic rather than manipulative, victims frequently fail to recognize the danger until the compromise is complete, at which point attackers leverage the situation for ongoing blackmail and continuous data access.
Practical Red Flags and Warning Signs for Technology Firms
Recognizing subtle behavioral manipulation remains difficult because victims often perceive the manufactured interactions as genuine professional luck or personal connection. However, security specialists recommend monitoring specific indicators that suggest a potential compromise or targeted recruitment attempt. A primary warning sign involves coincidental encounters that occur with unusual frequency, accompanied by persistent and intrusive curiosity regarding internal company details, requests for strict secrecy regarding meetings, and aggressive pressure for professional introductions.
Brown suggested a simple evaluation method for founders and employees, advising them to consider whether a particular contact would remain present if they lost their professional position the following day. Carpenter added that the most significant indicator of danger arises when an individual gradually escalates their requests, pushing past personal and professional boundaries that the target would normally enforce under standard circumstances.
Strengthening Corporate Security Culture and Governance
Addressing these vulnerabilities requires a fundamental shift in how technology firms approach internal security and organizational hierarchy. Carpenter stressed the urgent need for leadership teams to eliminate executive exceptionalism, which assumes that standard security policies and monitoring rules do not apply to individuals holding high positions of power. Cultivating an open environment where employees feel empowered to question unusual or suspicious behavior from top executives remains a vital defensive measure.
Brown emphasized that the rapid commercial expansion of the artificial intelligence sector outpaced the development of its internal security culture. Because victims of advanced social engineering rarely realize they are being manipulated, organizations must proactively establish clear communication channels and rigorous compliance frameworks to protect proprietary technology from evolving foreign and domestic threats.