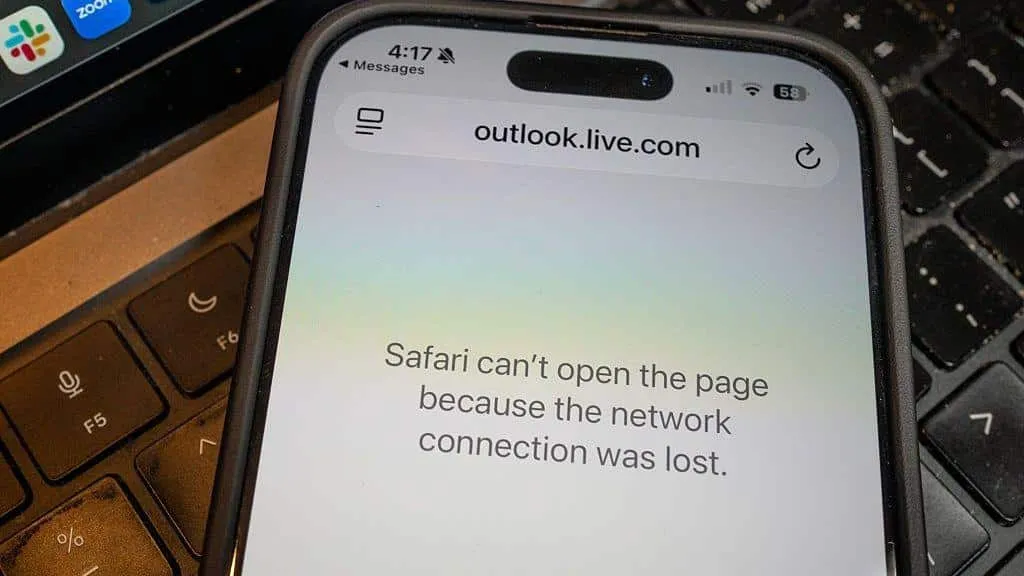
Microsoft's global service outage continued into Friday, November 13, disrupting Outlook, Teams, SharePoint, Copilot and other Microsoft 365 services while raising fresh concerns about online fraud and business data security.
The disruption began on Thursday evening and remained unresolved as businesses started work on Friday. Microsoft said its recovery efforts were not progressing as expected because some servers remained in an unstable state and changes were not synchronising properly.
The company said it had identified a problem involving an overloaded server process responsible for handling secure connections. It began rolling back a network configuration change and adjusting traffic distribution to restore services.
Microsoft said there was no indication that the outage was caused by a cyberattack. However, it had not provided a confirmed timeline for complete restoration.
What Caused the Outage and How Microsoft Is Responding
According to the company, a core server process that manages encrypted connections became overloaded during a routine network configuration update. The overload prevented the process from handling new traffic, leading to a cascade of failures across the Microsoft 365 stack.
Engineers responded by reverting the recent configuration change and rebalancing traffic across data centres. The rollback is intended to relieve pressure on the affected servers and allow normal synchronisation of user data.
Microsoft's status page indicated that the rollback was still in progress on Friday and that some services remained in a degraded state. No external threat was identified, and the firm reiterated that the issue appears to be purely technical.
How the Outage Is Affecting Daily Business Operations
Outages of Outlook, Teams and SharePoint strike at the heart of most modern workplaces. Email, instant messaging, file sharing and collaborative editing are all built on the same platform. When the platform goes offline, employees lose access to calendars, meeting invites, shared documents and internal communication channels.
Companies that rely on Microsoft 365 for authentication also face secondary problems. Many cloud-based applications use Azure Active Directory or email-based sign-in, so an interruption can block access to third-party tools, ERP systems and customer-relationship platforms.
Financial analysts estimate that downtime of this magnitude can cost large enterprises thousands of dollars per hour in lost productivity, delayed orders and missed deadlines.
Scammers Exploit the Outage
The disruption has created opportunities for fraudsters posing as Microsoft employees or technical support representatives.
Banks and financial organisations have warned customers about fake calls offering to repair Microsoft-related problems. Scammers may attempt to gain remote access to computers, steal personal information or persuade users to disclose sensitive details.
ING warned customers against allowing unsolicited callers to access their devices without first verifying their identity through an organisation's publicly listed contact number.
Financial crime experts have also warned that criminals could switch to phone calls and other communication channels when email services are unavailable. These attempts could continue even after Microsoft's systems return to normal.
Data-Security Risks From Unofficial Workarounds
The outage has also raised concerns about employees using unofficial methods to continue working while Microsoft services remain unavailable.
Workers may turn to personal email accounts, WhatsApp or unapproved applications to exchange business documents and customer information. Such workarounds could expose confidential data and create additional cybersecurity risks.
Businesses have also faced problems accessing other systems that rely on email-based authentication, highlighting their dependence on Microsoft's services.
Potential Financial Impact and Insurance Considerations
The disruption could create financial losses for companies through missed orders, delayed transactions and lost working hours.
Insurance coverage may not automatically compensate businesses for these losses. Cyber-insurance policies often contain specific conditions, waiting periods and limits for disruptions involving external technology providers.
What Companies Can Do Right Now
Experts recommend that organisations communicate clearly with staff about approved alternative channels, such as corporate-approved file-sharing portals or temporary VPN access, to limit exposure to insecure tools.
IT departments should audit any ad-hoc solutions that appear during the outage and remove them once Microsoft services are restored. Updating incident-response plans to include cloud-service failures can also reduce future risk.
What to Watch for in the Coming Days
Microsoft has said it will continue to monitor the situation and provide updates on its status page. Stakeholders should watch for a formal post-mortem report that details the root cause, the timeline of corrective actions and any changes to the company's change-management procedures.
Regulators may also seek explanations if the outage leads to significant data-privacy breaches or consumer-impact complaints. Businesses should be prepared to respond to inquiries from auditors or compliance officers regarding any data that may have been transmitted through unofficial channels during the downtime.