Italy Penalises Meta Platforms Ireland Over Android Photo Access
Italy has fined Meta €805 million, which translates to around $887 million, for letting the Facebook application on Android mobile devices access user photographs, video files, and associated metadata without obtaining proper consent. Italy's data protection authority, known as the Garante, announced this substantial monetary penalty against Meta Platforms Ireland on Saturday. According to the regulatory body, the technology giant failed to secure specific consent from Italian citizens or adequately inform them regarding the ways their smartphone media libraries were being processed and used by the software.
This enforcement action marks one of the largest regulatory penalties imposed on the corporation in Europe, reflecting mounting scrutiny over how major technology companies handle personal data. The penalty amount equals about 0.47 percent of the global corporate turnover of the group. The investigation into these practices began in July 2025 following a formal complaint filed by a consumer protection group based in Bolzano.
Understanding the Facebook Gallery Feature Violation
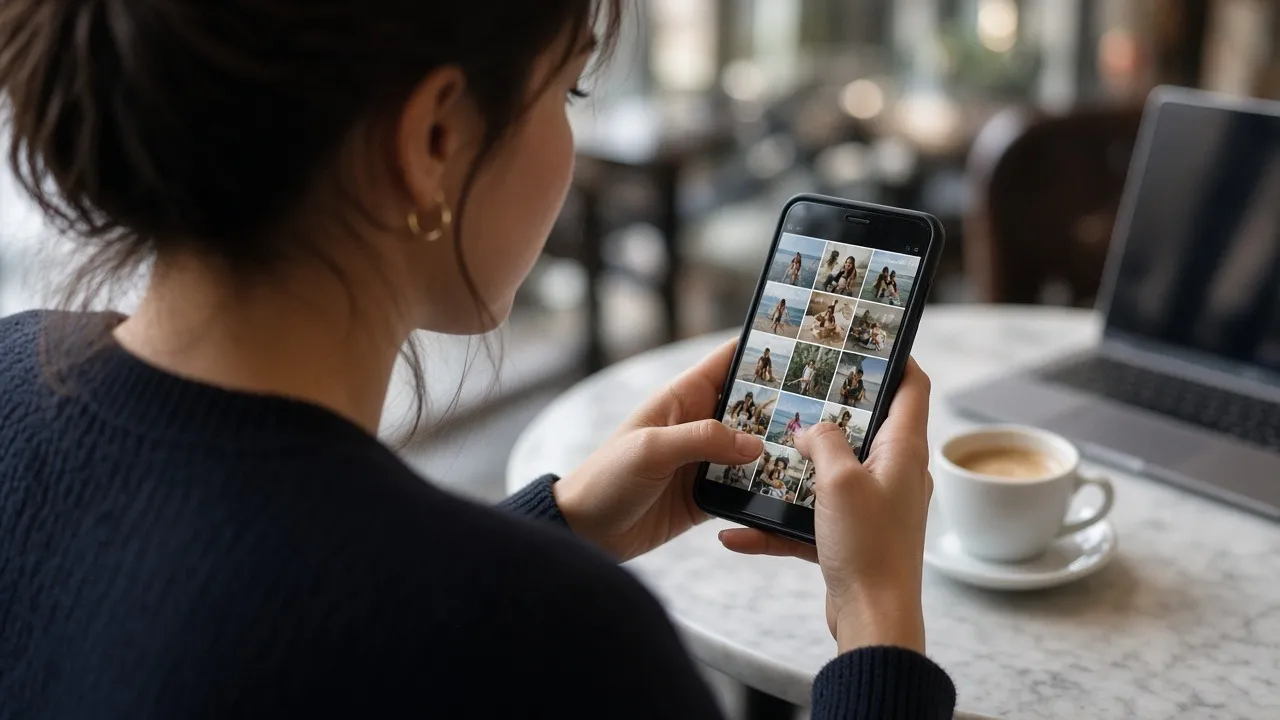
The regulatory case centres entirely around a specific Facebook software capability titled Get suggestions from gallery when browsing Facebook, which has been active since the year 2023. While individuals scroll through their social media feeds, this mechanism proposes pictures and recorded clips from their local device storage as potential ideas for creating fresh posts. The Garante established that this functionality operated by requesting full storage permissions through a broad, single prompt that covered the entire mobile application along with several completely unrelated functions.
During the permission prompt process, the warning shown to users spoke only vaguely about enabling other features, meaning individuals had no realistic way to understand that they were simultaneously granting permission for gallery suggestions. Furthermore, this intrusive data-gathering capability was switched on automatically by default as soon as the broader permission was granted. Once access was secured in this manner, the application could read a phone entire photo library, usually on a permanent basis, leaving neither the affected individuals nor the regulatory inspectors able to verify what content was actually accessed or used.
Strict Compliance Deadlines and Corrective Measures Ordered
Under the terms issued by the Italian data authority, Meta faces a strict 60 day deadline to turn the offending feature off by default for all users, including those who had previously granted permission. The company must also establish a separate, clear request process that explains precisely what the capability does and provides clear instructions on how to disable it. Additionally, the corporation is required to report its preliminary steps to the regulator within 30 days and present its final compliance measures within a 90 day window.
The Garante explained that the size of the financial penalty reflects the approximately 20 million Android users affected within Italy. Regulators also factored in that the legal violation remains ongoing for many of those individuals, noted a previous 2019 legal ruling against the enterprise, and cited poor cooperation from the company throughout the course of the investigation.
Broader Context of European Privacy Regulations and AI Scrutiny
European data protection laws strictly mandate that consent must be freely given, specific, informed, and unambiguous. Regulators across the continent have repeatedly cracked down on dark patterns and bundled consent mechanisms where companies hide data collection behind broad terms of service or multi-purpose permissions. When mobile applications request broad hardware access, such as reading local storage or device directories, privacy authorities expect explicit separation of permissions so that consumers retain absolute control over sensitive personal assets like photo libraries.
Although the recent investigation did not examine whether the harvested media content was deployed to train artificial intelligence models, a practice that Meta denies undertaking, the Garante noted that it may separately review a newly introduced 2026 feature that processes gallery content directly within cloud infrastructure. This distinction highlights the growing intersection between traditional privacy compliance and emerging computational technologies.
Corporate Response and History of Regulatory Penalties in Europe
In response to the announcement, representatives for Meta stated that the corporation will appeal the decision, describing the multimillion-euro financial penalty as disproportionate. The technology conglomerate has frequently clashed with European regulators and has encountered numerous heavy financial penalties on the continent in past years. Notable past enforcement actions include a record $1.3 billion fine levied for transferring European user information across the Atlantic to servers located in the United States. The company also recently chose to suspend a Muse artificial intelligence sharing feature due to separate ongoing privacy concerns raised by authorities.
For millions of citizens, this case serves as a stark reminder of the hidden data-sharing mechanisms embedded within popular smartphone software. As regulatory bodies continue to flex their enforcement powers under strict legislative frameworks, technology firms face intense pressure to overhaul how they present permission requests and handle personal media storage libraries.