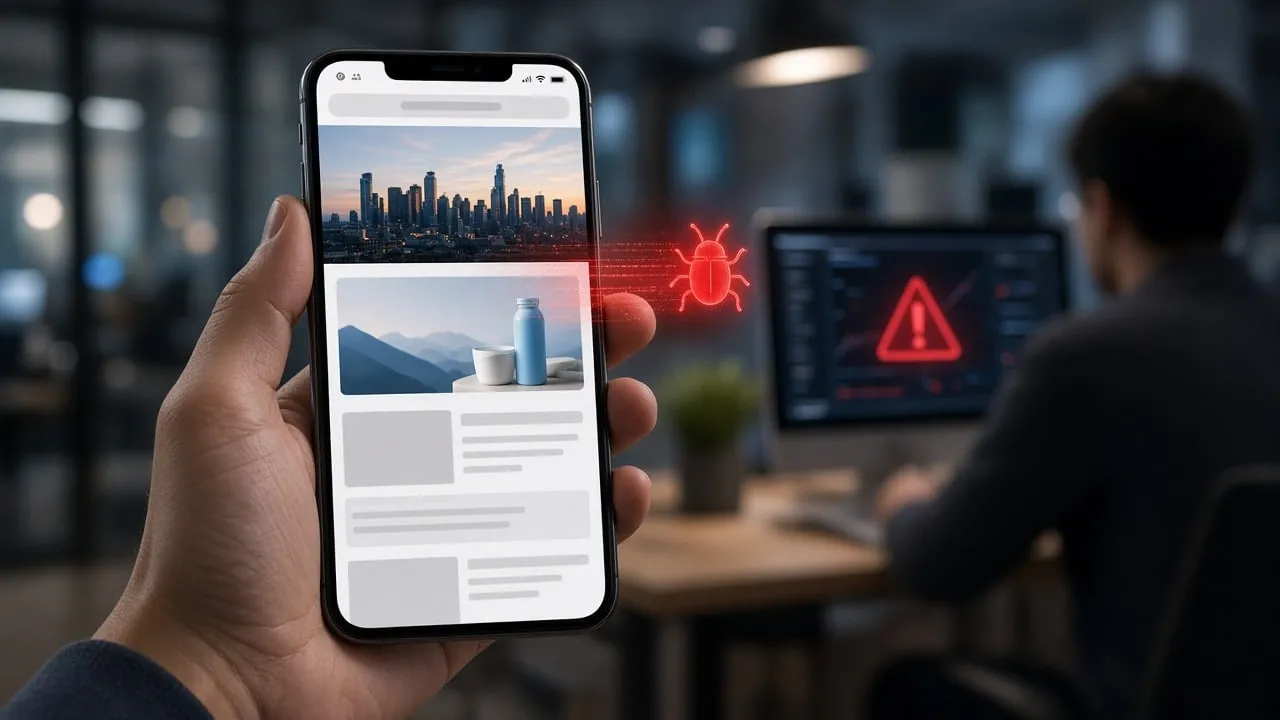
Mobile devices face spyware infections merely by loading an online ad, requiring no user clicks, according to a warning issued by the National Cyber Emergency Response Team, known as National CERT.
During a recent advisory, National CERT explained that malicious actors are abusing digital advertising networks to aim at mobile devices. Users do not need to open an attachment, press a suspicious link, or perform any action for the compromise to succeed.
What Is AdFection
The advisory highlighted a method called "AdFection." This tactic allows attackers to abuse digital advertising platforms to build user profiles and push mercenary spyware via advertisements displayed on mobile applications and websites.
This alert stems from research released by Citizen Lab on October 15, 2026. The same study revealed that Pakistan ranked among the primary targets in this ad-based spyware operation.
Based on the advisory, Citizen Lab recorded a high-confidence discovery that devices belonging to Al Jazeera were targeted and infected with Candiru spyware through this exact technique.
The assault can entail pushing malicious code via ads, choosing specific devices, and taking advantage of vulnerabilities in operating systems, browsers, or apps to secure entry.
National CERT pointed out, however, that merely viewing an advertisement does not guarantee a device has faced targeting or compromise.
What Is at Risk
National CERT cautioned that a successful breach can reveal personal messages, photographs, documents, account passwords, and additional confidential information.
The organization also highlighted dangers involving unauthorized spying, complete device control, and leaks concerning government, corporate, research, and media data. The extent of the harm relies on the specific flaws targeted, the software version of the device, and the functions of the spyware.
How to Stay Safe
National CERT recommended that users take the following steps:
- Keep operating systems, browsers, and apps updated
- Use devices that still receive regular security updates
- Install apps only from trusted sources
- Turn on multi-factor authentication for important accounts
Entities were instructed to weigh ad-blocking and browser-level safeguards, maintain security logs, improve device tracking, and request expert digital forensics assistance if they suspect an issue.
The organization, which recently cautioned personnel regarding a separate security threat, noted that reliable indicators of spyware operations or focused cyber attacks can be submitted via its official incident-reporting channel.